mirror of
https://github.com/fairyglade/ly.git
synced 2026-11-07 18:51:48 +00:00
Compare commits
73
Commits
| Author | SHA1 | Date | |
|---|---|---|---|
 Leon Grünewald |
271b4f8898 | ||
|
Leon Grünewald
|
552d533435 | ||
|
Leon Grünewald
|
9d774d93c5 | ||
|
Leon Grünewald
|
90f18e9b34 | ||
|
Leon Grünewald
|
ccb9dfabc5 | ||
|
Leon Grünewald
|
4ba42400ce | ||
|
Leon Grünewald
|
b336b70605 | ||
|
Leon Grünewald
|
9c70ff5576 | ||
|
Leon Grünewald
|
ec230541f3 | ||
|
Leon Grünewald
|
d2fcb2e87d | ||
|
Leon Grünewald
|
96a556a345 | ||
|
Leon Grünewald
|
f79330cda3 | ||
|
Leon Grünewald
|
3deedba040 | ||
|
Leon Grünewald
|
dfe918358e | ||
|
Leon Grünewald
|
cd738eafa7 | ||
|
Leon Grünewald
|
289624bc88 | ||
|
Leon Grünewald
|
7d4b25fc70 | ||
|
Leon Grünewald
|
b8b31386e1 | ||
|
Leon Grünewald
|
a14e6b5224 | ||
|
Leon Grünewald
|
16922531e2 | ||
|
Leon Grünewald
|
5c04c996d5 | ||
|
Leon Grünewald
|
a7dedbab1b | ||
|
Leon Grünewald
|
1926901eda | ||
|
Leon Grünewald
|
43a40faf79 | ||
|
Leon Grünewald
|
974aca51cb | ||
|
Leon Grünewald
|
6ac03ab27e | ||
 nullgemm |
77f6958241 | ||
|
nullgemm
|
1523d0858d | ||
|
nullgemm
|
f6658f83a9 | ||
 tyusha0 |
52d24304f8 | ||
 Deven Blake |
ab531c9b2d | ||
|
nullgemm
|
86bd5bc1f6 | ||
|
nullgemm
|
7e7b2adf05 | ||
|
nullgemm
|
8493c5a8ad | ||
|
nullgemm
|
4a7c82e3e3 | ||
 Egor Duplensky |
0a0da30ac9 | ||
|
nullgemm
|
c0328b3677 | ||
 Mihai Morariu |
29e3ac28dd | ||
 Érico Nogueira Rolim |
ce74c762ee | ||
|
nullgemm
|
afb6e964dd | ||
|
nullgemm
|
ce785ed0dc | ||
|
nullgemm
|
915ebd442f | ||
|
nullgemm
|
825544f7e2 | ||
|
Érico Nogueira Rolim
|
33934f3ab2 | ||
|
nullgemm
|
4882cd4548 | ||
|
nullgemm
|
36b7ab0d4d | ||
|
nullgemm
|
9eb212cb91 | ||
|
Érico Nogueira Rolim
|
fa42781cb9 | ||
|
Deven Blake
|
740e7393bb | ||
 mozartilize |
ccf7911e9f | ||
 Iván |
faff4d21f0 | ||
|
nullgemm
|
3d2ec52290 | ||
|
nullgemm
|
4a1adf92b5 | ||
|
Iván
|
7904b07e14 | ||
|
nullgemm
|
c83ef00099 | ||
 Stuart Reilly |
37fc47ef7a | ||
 Mateusz Piotrowski |
4d0549d53a | ||
 Stanislav Láznička |
a99c18b7fa | ||
|
Stanislav Láznička
|
ecaea4131b | ||
 Roosemberth Palacios |
31e1ba84af | ||
|
Roosemberth Palacios
|
f650e82f93 | ||
|
Roosemberth Palacios
|
fe4af2bfe6 | ||
|
Stanislav Láznička
|
9486f05e59 | ||
|
Stanislav Láznička
|
95c0077416 | ||
|
nullgemm
|
6388208bb1 | ||
|
nullgemm
|
ce07938ccf | ||
|
nullgemm
|
3c20d7d47c | ||
|
nullgemm
|
7457ceaa56 | ||
|
nullgemm
|
500951fa34 | ||
|
nullgemm
|
bce0a161af | ||
|
nullgemm
|
e5cb2b4cf8 | ||
|
nullgemm
|
efc5c49de5 | ||
|
nullgemm
|
303a80dae8 |
No files matched your search
@@ -0,0 +1,4 @@
|
||||
srpm:
|
||||
cd $(spec)
|
||||
make github
|
||||
rpmbuild -vv -bs ly.spec --define "_srcrpmdir $(outdir)"
|
||||
@@ -1,15 +1,15 @@
|
||||
[submodule "sub/argoat"]
|
||||
path = sub/argoat
|
||||
url = https://git.cylgom.net/cylgom/argoat.git
|
||||
url = https://git.nullgemm.fr/nullgemm/argoat.git
|
||||
[submodule "sub/configator"]
|
||||
path = sub/configator
|
||||
url = https://git.cylgom.net/cylgom/configator.git
|
||||
url = https://git.nullgemm.fr/nullgemm/configator.git
|
||||
[submodule "sub/ctypes"]
|
||||
path = sub/ctypes
|
||||
url = https://git.cylgom.net/cylgom/ctypes.git
|
||||
url = https://git.nullgemm.fr/nullgemm/ctypes.git
|
||||
[submodule "sub/dragonfail"]
|
||||
path = sub/dragonfail
|
||||
url = https://git.cylgom.net/cylgom/dragonfail.git
|
||||
url = https://git.nullgemm.fr/nullgemm/dragonfail.git
|
||||
[submodule "sub/termbox_next"]
|
||||
path = sub/termbox_next
|
||||
url = https://git.cylgom.net/cylgom/termbox_next.git
|
||||
url = https://git.nullgemm.fr/nullgemm/termbox_next.git
|
||||
@@ -1,15 +1,15 @@
|
||||
[submodule "sub/argoat"]
|
||||
path = sub/argoat
|
||||
url = https://github.com/cylgom/argoat.git
|
||||
url = https://github.com/nullgemm/argoat.git
|
||||
[submodule "sub/configator"]
|
||||
path = sub/configator
|
||||
url = https://github.com/cylgom/configator.git
|
||||
url = https://github.com/nullgemm/configator.git
|
||||
[submodule "sub/ctypes"]
|
||||
path = sub/ctypes
|
||||
url = https://github.com/cylgom/ctypes.git
|
||||
url = https://github.com/nullgemm/ctypes.git
|
||||
[submodule "sub/dragonfail"]
|
||||
path = sub/dragonfail
|
||||
url = https://github.com/cylgom/dragonfail.git
|
||||
url = https://github.com/nullgemm/dragonfail.git
|
||||
[submodule "sub/termbox_next"]
|
||||
path = sub/termbox_next
|
||||
url = https://github.com/cylgom/termbox_next.git
|
||||
url = https://github.com/nullgemm/termbox_next.git
|
||||
@@ -0,0 +1,78 @@
|
||||
%define relabel_files() \
|
||||
restorecon -R /usr/bin/ly; \
|
||||
|
||||
%define selinux_policyver 3.14.6-34
|
||||
|
||||
Name: {{{ git_dir_name }}}
|
||||
Version: {{{ git_dir_version }}}
|
||||
Release: 1%{?dist}
|
||||
Summary: A TUI display manager
|
||||
License: WTFPL
|
||||
URL: https://github.com/nullgemm/ly
|
||||
VCS: {{{ git_dir_vcs }}}
|
||||
Source: {{{ git_dir_pack }}}
|
||||
BuildRequires: libxcb-devel
|
||||
BuildRequires: pam-devel
|
||||
BuildRequires: make
|
||||
BuildRequires: git
|
||||
BuildRequires: gcc
|
||||
BuildRequires: selinux-policy-devel
|
||||
Requires: libxcb
|
||||
Requires: pam
|
||||
|
||||
%description
|
||||
Ly is a lightweight TUI (ncurses-like) display manager for Linux and BSD.
|
||||
|
||||
%prep
|
||||
git clone https://github.com/dhalucario/ly.git ly
|
||||
cd ly
|
||||
# git checkout v0.5.2
|
||||
make github
|
||||
|
||||
%build
|
||||
cd ly
|
||||
make
|
||||
|
||||
%install
|
||||
cd ly
|
||||
mkdir -p %{buildroot}/etc/
|
||||
mkdir -p %{buildroot}/usr/bin/
|
||||
mkdir -p %{buildroot}/usr/lib/systemd/system/
|
||||
mkdir -p %{buildroot}/etc/pam.d/
|
||||
DESTDIR="%{buildroot}" make install
|
||||
DESTDIR="%{buildroot}" make installselinux
|
||||
chmod -x %{buildroot}/etc/ly/config.ini
|
||||
chmod -x %{buildroot}/etc/ly/lang/*
|
||||
|
||||
%post
|
||||
semodule -n -i /usr/share/selinux/packages/ly.pp
|
||||
if /usr/sbin/selinuxenabled ; then
|
||||
/usr/sbin/load_policy
|
||||
%relabel_files
|
||||
|
||||
fi;
|
||||
exit 0
|
||||
|
||||
%postun
|
||||
if [ $1 -eq 0 ]; then
|
||||
semodule -n -r ly
|
||||
fi;
|
||||
exit 0
|
||||
|
||||
%files
|
||||
/usr/bin/ly
|
||||
/usr/lib/systemd/system/ly.service
|
||||
/etc/ly/lang/es.ini
|
||||
/etc/ly/lang/pt.ini
|
||||
/etc/ly/lang/ru.ini
|
||||
/etc/ly/lang/en.ini
|
||||
/etc/ly/lang/fr.ini
|
||||
/etc/ly/lang/ro.ini
|
||||
/etc/ly/xsetup.sh
|
||||
/etc/ly/wsetup.sh
|
||||
/etc/ly/config.ini
|
||||
/etc/pam.d/ly
|
||||
/usr/share/selinux/packages/ly.pp
|
||||
|
||||
%changelog
|
||||
{{{ git_dir_changelog }}}
|
||||
@@ -1,7 +1,7 @@
|
||||
NAME = ly
|
||||
CC = gcc
|
||||
FLAGS = -std=c99 -pedantic -g
|
||||
FLAGS+= -Wall -Wno-unused-parameter -Wextra -Werror=vla -Werror
|
||||
FLAGS+= -Wall -Wextra -Werror=vla -Wno-unused-parameter
|
||||
#FLAGS+= -DDEBUG
|
||||
FLAGS+= -DGIT_VERSION_STRING=\"$(shell git describe --long --tags | sed 's/\([^-]*-g\)/r\1/;s/-/./g')\"
|
||||
LINK = -lpam -lxcb
|
||||
@@ -20,6 +20,9 @@ SUBD = sub
|
||||
RESD = res
|
||||
TESTD = tests
|
||||
|
||||
DATADIR ?= ${DESTDIR}/etc/ly
|
||||
FLAGS+= -DDATADIR=\"$(DATADIR)\"
|
||||
|
||||
INCL = -I$(SRCD)
|
||||
INCL+= -I$(SUBD)/ctypes
|
||||
INCL+= -I$(SUBD)/argoat/src
|
||||
@@ -70,24 +73,48 @@ install: $(BIND)/$(NAME)
|
||||
@echo "installing"
|
||||
@install -dZ ${DESTDIR}/etc/ly
|
||||
@install -DZ $(BIND)/$(NAME) -t ${DESTDIR}/usr/bin
|
||||
@install -DZ $(RESD)/xsetup.sh -t ${DESTDIR}/etc/ly
|
||||
@install -DZ $(RESD)/wsetup.sh -t ${DESTDIR}/etc/ly
|
||||
@install -DZ $(RESD)/config.ini -t ${DESTDIR}/etc/ly
|
||||
@install -dZ ${DESTDIR}/etc/ly/lang
|
||||
@install -DZ $(RESD)/lang/* -t ${DESTDIR}/etc/ly/lang
|
||||
@install -DZ $(RESD)/ly.service -t ${DESTDIR}/usr/lib/systemd/system
|
||||
@install -DZ $(RESD)/xsetup.sh -t $(DATADIR)
|
||||
@install -DZ $(RESD)/wsetup.sh -t $(DATADIR)
|
||||
@install -dZ $(DATADIR)/lang
|
||||
@install -DZ $(RESD)/lang/* -t $(DATADIR)/lang
|
||||
@install -DZ $(RESD)/ly.service -m 644 -t ${DESTDIR}/usr/lib/systemd/system
|
||||
@install -DZ $(RESD)/pam.d/ly -m 644 -t ${DESTDIR}/etc/pam.d
|
||||
|
||||
installnoconf: $(BIND)/$(NAME)
|
||||
@echo "installing without the configuration file"
|
||||
@install -dZ ${DESTDIR}/etc/ly
|
||||
@install -DZ $(BIND)/$(NAME) -t ${DESTDIR}/usr/bin
|
||||
@install -DZ $(RESD)/xsetup.sh -t $(DATADIR)
|
||||
@install -DZ $(RESD)/wsetup.sh -t $(DATADIR)
|
||||
@install -dZ $(DATADIR)/lang
|
||||
@install -DZ $(RESD)/lang/* -t $(DATADIR)/lang
|
||||
@install -DZ $(RESD)/ly.service -m 644 -t ${DESTDIR}/usr/lib/systemd/system
|
||||
@install -DZ $(RESD)/pam.d/ly -m 644 -t ${DESTDIR}/etc/pam.d
|
||||
|
||||
installselinux:
|
||||
@echo "installing selinux modules"
|
||||
@make -f /usr/share/selinux/devel/Makefile ly.pp
|
||||
@install -DZ ly.pp ${DESTDIR}/usr/share/selinux/packages/ly.pp
|
||||
|
||||
uninstall:
|
||||
@echo "uninstalling"
|
||||
@rm -rf ${DESTDIR}/etc/ly
|
||||
@rm -rf $(DATADIR)
|
||||
@rm -f ${DESTDIR}/usr/bin/ly
|
||||
@rm -f ${DESTDIR}/usr/lib/systemd/system/ly.service
|
||||
@rm -f ${DESTDIR}/etc/pam.d/ly
|
||||
|
||||
clean:
|
||||
@echo "cleaning"
|
||||
@rm -rf $(BIND) $(OBJD) valgrind.log
|
||||
@(cd $(SUBD)/termbox_next && $(MAKE) clean)
|
||||
|
||||
remotes:
|
||||
@echo "registering remotes"
|
||||
@git remote add github git@github.com:nullgemm/$(NAME).git
|
||||
@git remote add gitea ssh://git@git.nullgem.fr:2999/nullgemm/$(NAME).git
|
||||
|
||||
github:
|
||||
@echo "sourcing submodules from https://github.com"
|
||||
@cp .github .gitmodules
|
||||
@@ -97,7 +124,7 @@ github:
|
||||
@git submodule update --init --recursive --remote
|
||||
|
||||
gitea:
|
||||
@echo "sourcing submodules from https://git.cylgom.net"
|
||||
@echo "sourcing submodules from personal server"
|
||||
@cp .gitea .gitmodules
|
||||
@git submodule sync
|
||||
@git submodule update --init --remote
|
||||
|
||||
@@ -1,13 +1,12 @@
|
||||
# Ly - a TUI display manager
|
||||
[](https://www.codefactor.io/repository/github/cylgom/ly/overview/master)
|
||||

|
||||
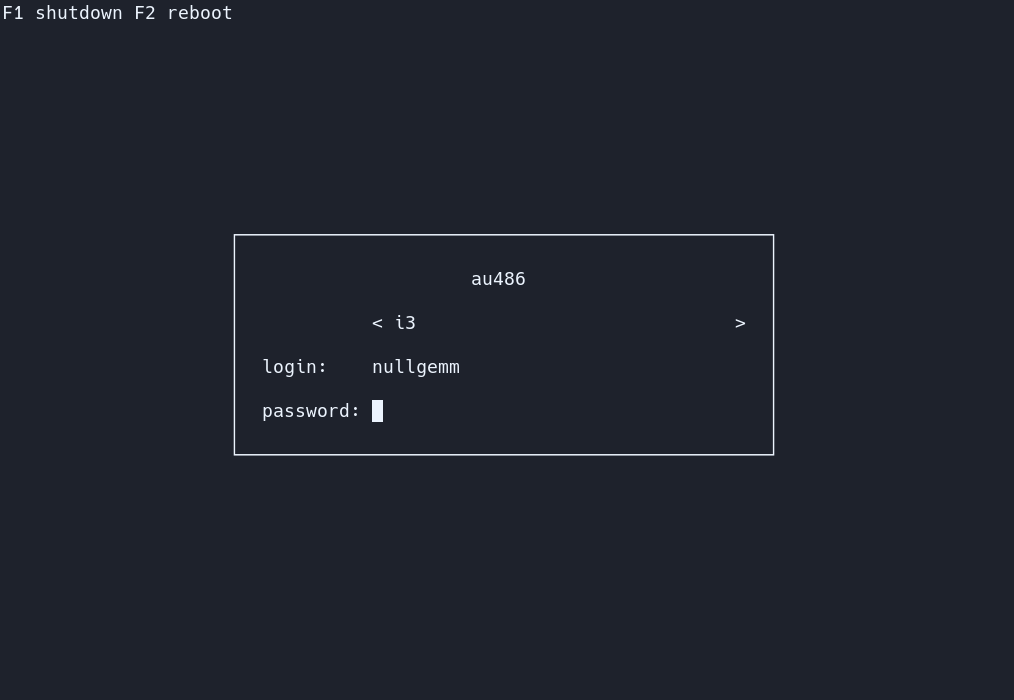
|
||||
|
||||
Ly is a lightweight TUI (ncurses-like) display manager for Linux and BSD.
|
||||
|
||||
## Dependencies
|
||||
- a C99 compiler (tested with tcc and gcc)
|
||||
- a C standard library
|
||||
- make
|
||||
- GNU make
|
||||
- pam
|
||||
- xcb
|
||||
- xorg
|
||||
@@ -16,6 +15,8 @@ Ly is a lightweight TUI (ncurses-like) display manager for Linux and BSD.
|
||||
- tput
|
||||
- shutdown
|
||||
|
||||
On Debian-based distros running `apt install build-essential libpam0g-dev libxcb-xkb-dev` as root should install all the dependencies for you.
|
||||
|
||||
## Support
|
||||
The following desktop environments were tested with success
|
||||
- budgie
|
||||
@@ -31,6 +32,8 @@ The following desktop environments were tested with success
|
||||
- sway
|
||||
- xfce
|
||||
- pantheon
|
||||
- maxx
|
||||
- windowmaker
|
||||
|
||||
Ly should work with any X desktop environment, and provides
|
||||
basic wayland support (sway works very well, for example).
|
||||
@@ -44,7 +47,7 @@ changing the source code won't be necessary :)
|
||||
## Cloning and Compiling
|
||||
Clone the repository
|
||||
```
|
||||
git clone https://github.com/cylgom/ly.git
|
||||
git clone https://github.com/nullgemm/ly.git
|
||||
```
|
||||
|
||||
Fetch submodules
|
||||
@@ -88,6 +91,19 @@ Use the up and down arrow keys to change the current field, and the
|
||||
left and right arrow keys to change the target desktop environment
|
||||
while on the desktop field (above the login field).
|
||||
|
||||
## .xinitrc
|
||||
If your .xinitrc doesn't work make sure it is executable and includes a shebang.
|
||||
This file is supposed to be a shell script! Quoting from xinit's man page:
|
||||
```
|
||||
If no specific client program is given on the command line, xinit will look for
|
||||
a file in the user's home directory called .xinitrc to run as a shell script to
|
||||
start up client programs.
|
||||
```
|
||||
On ArchLinux, the example .xinitrc (/etc/X11/xinit/xinitrc) starts like this:
|
||||
```
|
||||
#!/bin/sh
|
||||
```
|
||||
|
||||
## Tips
|
||||
The numlock and capslock state is printed in the top-right corner.
|
||||
Use the F1 and F2 keys to respectively shutdown and reboot.
|
||||
|
||||
+8
-3
@@ -16,6 +16,7 @@
|
||||
#blank_box = true
|
||||
|
||||
# erase password input on failure
|
||||
#blank_password = false
|
||||
#blank_password = true
|
||||
|
||||
# console path
|
||||
@@ -57,7 +58,7 @@
|
||||
#min_refresh_delta = 5
|
||||
|
||||
# default path
|
||||
#path = /sbin:/bin:/usr/local/sbin:/usr/local/bin:/usr/bin:/usr/bin/env
|
||||
#path = /sbin:/bin:/usr/local/sbin:/usr/local/bin:/usr/bin:/usr/sbin
|
||||
|
||||
# command executed when pressing F2
|
||||
#restart_cmd = /sbin/shutdown -r now
|
||||
@@ -68,8 +69,8 @@
|
||||
# file in which to save and load the default desktop and login
|
||||
#save_file = /etc/ly/save
|
||||
|
||||
# service name (pam needs this set to login)
|
||||
#service_name = login
|
||||
# service name (set to ly to use the provided pam config file)
|
||||
#service_name = ly
|
||||
|
||||
# command executed when pressing F1
|
||||
#shutdown_cmd = /sbin/shutdown -a now
|
||||
@@ -83,6 +84,10 @@
|
||||
# wayland setup command
|
||||
#wayland_cmd = /etc/ly/wsetup.sh
|
||||
|
||||
# add wayland specifier to session names
|
||||
#wayland_specifier = false
|
||||
#wayland_specifier = true
|
||||
|
||||
# wayland desktop environments
|
||||
#waylandsessions = /usr/share/wayland-sessions
|
||||
|
||||
|
||||
@@ -0,0 +1,45 @@
|
||||
capslock = Bloq Mayús
|
||||
err_alloc = asignación de memoria fallida
|
||||
err_bounds = índice fuera de límites
|
||||
err_chdir = error al abrir la carpeta home
|
||||
err_console_dev = error al acceder a la consola
|
||||
err_dgn_oob = mensaje de registro
|
||||
err_domain = dominio inválido
|
||||
err_hostname = error al obtener el nombre de host
|
||||
err_mlock = error al bloquear la contraseña de memoria
|
||||
err_null = puntero nulo
|
||||
err_pam = error en la transacción pam
|
||||
err_pam_abort = transacción pam abortada
|
||||
err_pam_acct_expired = cuenta expirada
|
||||
err_pam_auth = error de autenticación
|
||||
err_pam_authinfo_unavail = error al obtener información del usuario
|
||||
err_pam_authok_reqd = token expirado
|
||||
err_pam_buf = error de la memoria intermedia
|
||||
err_pam_cred_err = error al establecer la credenciales
|
||||
err_pam_cred_expired = credenciales expiradas
|
||||
err_pam_cred_insufficient = credenciales insuficientes
|
||||
err_pam_cred_unavail = error al obtener credenciales
|
||||
err_pam_maxtries = se ha alcanzado el límite de intentos
|
||||
err_pam_perm_denied = permiso denegado
|
||||
err_pam_session = error de sesión
|
||||
err_pam_sys = error de sistema
|
||||
err_pam_user_unknown = usuario desconocido
|
||||
err_path = error al establecer la ruta
|
||||
err_perm_dir = error al cambiar el directorio actual
|
||||
err_perm_group = error al degradar los permisos del grupo
|
||||
err_perm_user = error al degradar los permisos del usuario
|
||||
err_pwnam = error al obtener la información del usuario
|
||||
err_user_gid = error al establecer el GID del usuario
|
||||
err_user_init = errpr al inicializar usuario
|
||||
err_user_uid = error al establecer el UID del usuario
|
||||
err_xsessions_dir = error al buscar la carpeta de sesiones
|
||||
err_xsessions_open = error al abrir la carpeta de sesiones
|
||||
f1 = F1 apagar
|
||||
f2 = F2 reiniciar
|
||||
login = iniciar sesion:
|
||||
logout = cerrar sesion
|
||||
numlock = Bloq Num
|
||||
password = contraseña:
|
||||
shell = shell
|
||||
wayland = wayland
|
||||
xinitrc = xinitrc
|
||||
@@ -0,0 +1,45 @@
|
||||
capslock = caixa alta
|
||||
err_alloc = alocação de memória malsucedida
|
||||
err_bounds = índice fora de limites
|
||||
err_chdir = não foi possível abrir o diretório home
|
||||
err_console_dev = não foi possível acessar o console
|
||||
err_dgn_oob = mensagem de log
|
||||
err_domain = domínio inválido
|
||||
err_hostname = não foi possível obter o nome do host
|
||||
err_mlock = bloqueio da memória de senha malsucedido
|
||||
err_null = ponteiro nulo
|
||||
err_pam = transação pam malsucedida
|
||||
err_pam_abort = transação pam abortada
|
||||
err_pam_acct_expired = conta expirada
|
||||
err_pam_auth = erro de autenticação
|
||||
err_pam_authinfo_unavail = não foi possível obter informações do usuário
|
||||
err_pam_authok_reqd = token expirada
|
||||
err_pam_buf = erro de buffer de memória
|
||||
err_pam_cred_err = erro para definir credenciais
|
||||
err_pam_cred_expired = credenciais expiradas
|
||||
err_pam_cred_insufficient = credenciais insuficientes
|
||||
err_pam_cred_unavail = não foi possível obter credenciais
|
||||
err_pam_maxtries = limite máximo de tentativas atingido
|
||||
err_pam_perm_denied = permissão negada
|
||||
err_pam_session = erro de sessão
|
||||
err_pam_sys = erro de sistema
|
||||
err_pam_user_unknown = usuário desconhecido
|
||||
err_path = não foi possível definir o caminho
|
||||
err_perm_dir = não foi possível alterar o diretório atual
|
||||
err_perm_group = não foi possível reduzir as permissões de grupo
|
||||
err_perm_user = não foi possível reduzir as permissões de usuário
|
||||
err_pwnam = não foi possível obter informações do usuário
|
||||
err_user_gid = não foi possível definir o GID do usuário
|
||||
err_user_init = não foi possível iniciar o usuário
|
||||
err_user_uid = não foi possível definir o UID do usuário
|
||||
err_xsessions_dir = não foi possível encontrar a pasta das sessões
|
||||
err_xsessions_open = não foi possível abrir a pasta das sessões
|
||||
f1 = F1 desligar
|
||||
f2 = F2 reiniciar
|
||||
login = conectar:
|
||||
logout = desconectado
|
||||
numlock = numlock
|
||||
password = senha:
|
||||
shell = shell
|
||||
wayland = wayland
|
||||
xinitrc = xinitrc
|
||||
@@ -0,0 +1,45 @@
|
||||
capslock = capslock
|
||||
|
||||
|
||||
|
||||
err_console_dev = nu s-a putut accesa consola
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
err_pam_abort = tranzacţie pam anulată
|
||||
err_pam_acct_expired = cont expirat
|
||||
err_pam_auth = eroare de autentificare
|
||||
err_pam_authinfo_unavail = nu s-au putut obţine informaţii despre utilizator
|
||||
err_pam_authok_reqd = token expirat
|
||||
err_pam_buf = eroare de memorie (buffer)
|
||||
err_pam_cred_err = nu s-au putut seta date de identificare (credentials)
|
||||
err_pam_cred_expired = datele de identificare (credentials) au expirat
|
||||
err_pam_cred_insufficient = date de identificare (credentials) insuficiente
|
||||
err_pam_cred_unavail = nu s-au putut obţine date de indentificare (credentials)
|
||||
err_pam_maxtries = s-a atins numărul maxim de încercări
|
||||
err_pam_perm_denied = acces interzis
|
||||
err_pam_session = eroare de sesiune
|
||||
err_pam_sys = eroare de sistem
|
||||
err_pam_user_unknown = utilizator necunoscut
|
||||
|
||||
err_perm_dir = nu s-a putut schimba dosarul (folder-ul) curent
|
||||
err_perm_group = nu s-a putut face downgrade permisiunilor de grup
|
||||
err_perm_user = nu s-a putut face downgrade permisiunilor de utilizator
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
|
||||
f1 = F1 opreşte sistemul
|
||||
f2 = F2 resetează
|
||||
login = utilizator:
|
||||
logout = opreşte sesiunea
|
||||
numlock = numlock
|
||||
password = parolă:
|
||||
shell = shell
|
||||
wayland = wayland
|
||||
xinitrc = xinitrc
|
||||
@@ -0,0 +1,45 @@
|
||||
capslock = capslock
|
||||
err_alloc = не удалось выделить память
|
||||
err_bounds = за пределами индекса
|
||||
err_chdir = не удалось открыть домашнюю папку
|
||||
err_console_dev = не удалось получить доступ к консоли
|
||||
err_dgn_oob = отладочное сообщение (log)
|
||||
err_domain = неверный домен
|
||||
err_hostname = не удалось получить имя хоста
|
||||
err_mlock = сбой блокировки памяти
|
||||
err_null = нулевой указатель
|
||||
err_pam = pam транзакция не удалась
|
||||
err_pam_abort = pam транзакция прервана
|
||||
err_pam_acct_expired = срок действия аккаунта истек
|
||||
err_pam_auth = ошибка аутентификации
|
||||
err_pam_authinfo_unavail = не удалось получить информацию о пользователе
|
||||
err_pam_authok_reqd = токен истек
|
||||
err_pam_buf = ошибка буфера памяти
|
||||
err_pam_cred_err = не удалось установить полномочия
|
||||
err_pam_cred_expired = полномочия истекли
|
||||
err_pam_cred_insufficient = недостаточо полномочий
|
||||
err_pam_cred_unavail = не удалось получить полномочия
|
||||
err_pam_maxtries = лимит попыток исчерпан
|
||||
err_pam_perm_denied = доступ запрещен
|
||||
err_pam_session = ошибка сессии
|
||||
err_pam_sys = системная ошибка
|
||||
err_pam_user_unknown = неизвестный пользователь
|
||||
err_path = не удалось установить путь
|
||||
err_perm_dir = не удалось изменить текущий каталог
|
||||
err_perm_group = не удалось понизить права доступа группы
|
||||
err_perm_user = не удалось понизить права доступа пользователя
|
||||
err_pwnam = не удалось получить информацию о пользователе
|
||||
err_user_gid = не удалось установить GID пользователя
|
||||
err_user_init = не удалось инициализировать пользователя
|
||||
err_user_uid = не удалось установить UID пользователя
|
||||
err_xsessions_dir = не удалось найти сессионную папку
|
||||
err_xsessions_open = не удалось открыть сессионную папку
|
||||
f1 = F1 выключить
|
||||
f2 = F2 перезагрузить
|
||||
login = логин:
|
||||
logout = logged out
|
||||
numlock = numlock
|
||||
password = пароль:
|
||||
shell = shell
|
||||
wayland = wayland
|
||||
xinitrc = xinitrc
|
||||
@@ -0,0 +1,6 @@
|
||||
#%PAM-1.0
|
||||
|
||||
auth include login
|
||||
account include login
|
||||
password include login
|
||||
session include login
|
||||
+99
-1
@@ -1,4 +1,102 @@
|
||||
#! /bin/sh
|
||||
# Xsession - run as user
|
||||
# Copyright (C) 2016 Pier Luigi Fiorini <pierluigi.fiorini@gmail.com>
|
||||
|
||||
~/.xsession
|
||||
# This file is extracted from kde-workspace (kdm/kfrontend/genkdmconf.c)
|
||||
# Copyright (C) 2001-2005 Oswald Buddenhagen <ossi@kde.org>
|
||||
|
||||
# Note that the respective logout scripts are not sourced.
|
||||
case $SHELL in
|
||||
*/bash)
|
||||
[ -z "$BASH" ] && exec $SHELL $0 "$@"
|
||||
set +o posix
|
||||
[ -f /etc/profile ] && . /etc/profile
|
||||
if [ -f $HOME/.bash_profile ]; then
|
||||
. $HOME/.bash_profile
|
||||
elif [ -f $HOME/.bash_login ]; then
|
||||
. $HOME/.bash_login
|
||||
elif [ -f $HOME/.profile ]; then
|
||||
. $HOME/.profile
|
||||
fi
|
||||
;;
|
||||
*/zsh)
|
||||
[ -z "$ZSH_NAME" ] && exec $SHELL $0 "$@"
|
||||
[ -d /etc/zsh ] && zdir=/etc/zsh || zdir=/etc
|
||||
zhome=${ZDOTDIR:-$HOME}
|
||||
# zshenv is always sourced automatically.
|
||||
[ -f $zdir/zprofile ] && . $zdir/zprofile
|
||||
[ -f $zhome/.zprofile ] && . $zhome/.zprofile
|
||||
[ -f $zdir/zlogin ] && . $zdir/zlogin
|
||||
[ -f $zhome/.zlogin ] && . $zhome/.zlogin
|
||||
emulate -R sh
|
||||
;;
|
||||
*/csh|*/tcsh)
|
||||
# [t]cshrc is always sourced automatically.
|
||||
# Note that sourcing csh.login after .cshrc is non-standard.
|
||||
xsess_tmp=`mktemp /tmp/xsess-env-XXXXXX`
|
||||
$SHELL -c "if (-f /etc/csh.login) source /etc/csh.login; if (-f ~/.login) source ~/.login; /bin/sh -c 'export -p' >! $xsess_tmp"
|
||||
. $xsess_tmp
|
||||
rm -f $xsess_tmp
|
||||
;;
|
||||
*/fish)
|
||||
[ -f /etc/profile ] && . /etc/profile
|
||||
xsess_tmp=`mktemp /tmp/xsess-env-XXXXXX`
|
||||
$SHELL --login -c "/bin/sh -c 'export -p' > $xsess_tmp"
|
||||
. $xsess_tmp
|
||||
rm -f $xsess_tmp
|
||||
;;
|
||||
*) # Plain sh, ksh, and anything we do not know.
|
||||
[ -f /etc/profile ] && . /etc/profile
|
||||
[ -f $HOME/.profile ] && . $HOME/.profile
|
||||
;;
|
||||
esac
|
||||
|
||||
[ -f /etc/xprofile ] && . /etc/xprofile
|
||||
[ -f $HOME/.xprofile ] && . $HOME/.xprofile
|
||||
|
||||
# run all system xinitrc shell scripts.
|
||||
if [ -d /etc/X11/xinit/xinitrc.d ]; then
|
||||
for i in /etc/X11/xinit/xinitrc.d/* ; do
|
||||
if [ -x "$i" ]; then
|
||||
. "$i"
|
||||
fi
|
||||
done
|
||||
fi
|
||||
|
||||
# Load Xsession scripts
|
||||
# OPTIONFILE, USERXSESSION, USERXSESSIONRC and ALTUSERXSESSION are required
|
||||
# by the scripts to work
|
||||
xsessionddir="/etc/X11/Xsession.d"
|
||||
OPTIONFILE=/etc/X11/Xsession.options
|
||||
USERXSESSION=$HOME/.xsession
|
||||
USERXSESSIONRC=$HOME/.xsessionrc
|
||||
ALTUSERXSESSION=$HOME/.Xsession
|
||||
|
||||
if [ -d "$xsessionddir" ]; then
|
||||
for i in `ls $xsessionddir`; do
|
||||
script="$xsessionddir/$i"
|
||||
echo "Loading X session script $script"
|
||||
if [ -r "$script" -a -f "$script" ] && expr "$i" : '^[[:alnum:]_-]\+$' > /dev/null; then
|
||||
. "$script"
|
||||
fi
|
||||
done
|
||||
fi
|
||||
|
||||
if [ -d /etc/X11/Xresources ]; then
|
||||
for i in /etc/X11/Xresources/*; do
|
||||
[ -f $i ] && xrdb -merge $i
|
||||
done
|
||||
elif [ -f /etc/X11/Xresources ]; then
|
||||
xrdb -merge /etc/X11/Xresources
|
||||
fi
|
||||
[ -f $HOME/.Xresources ] && xrdb -merge $HOME/.Xresources
|
||||
|
||||
if [ -f "$USERXSESSION" ]; then
|
||||
. "$USERXSESSION"
|
||||
fi
|
||||
|
||||
if [ -z "$*" ]; then
|
||||
exec xmessage -center -buttons OK:0 -default OK "Sorry, $DESKTOP_SESSION is no valid session."
|
||||
else
|
||||
exec $@
|
||||
fi
|
||||
@@ -0,0 +1 @@
|
||||
/usr/bin/ly -- gen_context(system_u:object_r:ly_exec_t,s0)
|
||||
@@ -0,0 +1,41 @@
|
||||
|
||||
## <summary>policy for ly</summary>
|
||||
|
||||
########################################
|
||||
## <summary>
|
||||
## Execute ly_exec_t in the ly domain.
|
||||
## </summary>
|
||||
## <param name="domain">
|
||||
## <summary>
|
||||
## Domain allowed to transition.
|
||||
## </summary>
|
||||
## </param>
|
||||
#
|
||||
interface(`ly_domtrans',`
|
||||
gen_require(`
|
||||
type ly_t, ly_exec_t;
|
||||
')
|
||||
|
||||
corecmd_search_bin($1)
|
||||
domtrans_pattern($1, ly_exec_t, ly_t)
|
||||
')
|
||||
|
||||
######################################
|
||||
## <summary>
|
||||
## Execute ly in the caller domain.
|
||||
## </summary>
|
||||
## <param name="domain">
|
||||
## <summary>
|
||||
## Domain allowed access.
|
||||
## </summary>
|
||||
## </param>
|
||||
#
|
||||
interface(`ly_exec',`
|
||||
gen_require(`
|
||||
type ly_exec_t;
|
||||
')
|
||||
|
||||
corecmd_search_bin($1)
|
||||
can_exec($1, ly_exec_t)
|
||||
')
|
||||
|
||||
Executable
+32
@@ -0,0 +1,32 @@
|
||||
policy_module(ly, 1.0.0)
|
||||
|
||||
########################################
|
||||
#
|
||||
# Declarations
|
||||
#
|
||||
|
||||
type ly_t;
|
||||
type ly_exec_t;
|
||||
init_daemon_domain(ly_t, ly_exec_t)
|
||||
|
||||
permissive ly_t;
|
||||
|
||||
########################################
|
||||
#
|
||||
# ly local policy
|
||||
#
|
||||
allow ly_t self:capability { setgid setuid };
|
||||
allow ly_t self:process { fork signal_perms };
|
||||
allow ly_t self:process transition;
|
||||
allow ly_t self:fifo_file rw_fifo_file_perms;
|
||||
allow ly_t self:unix_stream_socket create_stream_socket_perms;
|
||||
|
||||
domain_use_interactive_fds(ly_t)
|
||||
|
||||
files_read_etc_files(ly_t)
|
||||
|
||||
auth_use_nsswitch(ly_t)
|
||||
|
||||
logging_send_audit_msgs(ly_t)
|
||||
|
||||
miscfiles_read_localization(ly_t)
|
||||
+15
-9
@@ -9,7 +9,7 @@
|
||||
#include <unistd.h>
|
||||
|
||||
#ifndef DEBUG
|
||||
#define INI_LANG "/etc/ly/lang/%s.ini"
|
||||
#define INI_LANG DATADIR "/lang/%s.ini"
|
||||
#define INI_CONFIG "/etc/ly/config.ini"
|
||||
#else
|
||||
#define INI_LANG "../res/lang/%s.ini"
|
||||
@@ -146,8 +146,12 @@ void lang_load()
|
||||
}
|
||||
}
|
||||
|
||||
void config_load()
|
||||
void config_load(const char *cfg_path)
|
||||
{
|
||||
if (cfg_path == NULL)
|
||||
{
|
||||
cfg_path = INI_CONFIG;
|
||||
}
|
||||
// must be alphabetically sorted
|
||||
struct configator_param map_no_section[] =
|
||||
{
|
||||
@@ -156,7 +160,7 @@ void config_load()
|
||||
{"asterisk", &config.asterisk, config_handle_char},
|
||||
{"bg", &config.bg, config_handle_u8},
|
||||
{"blank_box", &config.blank_box, config_handle_bool},
|
||||
{"blank_password", &config.blank_box, config_handle_bool},
|
||||
{"blank_password", &config.blank_password, config_handle_bool},
|
||||
{"console_dev", &config.console_dev, config_handle_str},
|
||||
{"default_input", &config.default_input, config_handle_u8},
|
||||
{"fg", &config.fg, config_handle_u8},
|
||||
@@ -180,6 +184,7 @@ void config_load()
|
||||
{"term_reset_cmd", &config.term_reset_cmd, config_handle_str},
|
||||
{"tty", &config.tty, config_handle_u8},
|
||||
{"wayland_cmd", &config.wayland_cmd, config_handle_str},
|
||||
{"wayland_specifier", &config.wayland_specifier, config_handle_bool},
|
||||
{"waylandsessions", &config.waylandsessions, config_handle_str},
|
||||
{"x_cmd", &config.x_cmd, config_handle_str},
|
||||
{"x_cmd_setup", &config.x_cmd_setup, config_handle_str},
|
||||
@@ -202,7 +207,7 @@ void config_load()
|
||||
config.sections = sections;
|
||||
config.sections_len = sections_len;
|
||||
|
||||
configator(&config, INI_CONFIG);
|
||||
configator(&config, (char *) cfg_path);
|
||||
}
|
||||
|
||||
void lang_defaults()
|
||||
@@ -263,7 +268,7 @@ void config_defaults()
|
||||
config.blank_box = true;
|
||||
config.blank_password = false;
|
||||
config.console_dev = strdup("/dev/console");
|
||||
config.default_input = 2;
|
||||
config.default_input = PASSWORD_INPUT;
|
||||
config.fg = 9;
|
||||
config.hide_borders = false;
|
||||
config.input_len = 34;
|
||||
@@ -276,18 +281,19 @@ void config_defaults()
|
||||
config.max_password_len = 255;
|
||||
config.mcookie_cmd = strdup("/usr/bin/mcookie");
|
||||
config.min_refresh_delta = 5;
|
||||
config.path = strdup("/sbin:/bin:/usr/local/sbin:/usr/local/bin:/usr/bin:/usr/bin/env");
|
||||
config.path = strdup("/sbin:/bin:/usr/local/sbin:/usr/local/bin:/usr/bin:/usr/sbin");
|
||||
config.restart_cmd = strdup("/sbin/shutdown -r now");
|
||||
config.save = true;
|
||||
config.save_file = strdup("/etc/ly/save");
|
||||
config.service_name = strdup("login");
|
||||
config.service_name = strdup("ly");
|
||||
config.shutdown_cmd = strdup("/sbin/shutdown -a now");
|
||||
config.term_reset_cmd = strdup("/usr/bin/tput reset");
|
||||
config.tty = 2;
|
||||
config.wayland_cmd = strdup("/etc/ly/wsetup.sh");
|
||||
config.wayland_cmd = strdup(DATADIR "/wsetup.sh");
|
||||
config.wayland_specifier = false;
|
||||
config.waylandsessions = strdup("/usr/share/wayland-sessions");
|
||||
config.x_cmd = strdup("/usr/bin/X");
|
||||
config.x_cmd_setup = strdup("/etc/ly/xsetup.sh");
|
||||
config.x_cmd_setup = strdup(DATADIR "/xsetup.sh");
|
||||
config.xauth_cmd = strdup("/usr/bin/xauth");
|
||||
config.xsessions = strdup("/usr/share/xsessions");
|
||||
}
|
||||
|
||||
+8
-1
@@ -3,6 +3,12 @@
|
||||
|
||||
#include "ctypes.h"
|
||||
|
||||
enum INPUTS {
|
||||
SESSION_SWITCH,
|
||||
LOGIN_INPUT,
|
||||
PASSWORD_INPUT,
|
||||
};
|
||||
|
||||
struct lang
|
||||
{
|
||||
char* capslock;
|
||||
@@ -83,6 +89,7 @@ struct config
|
||||
char* term_reset_cmd;
|
||||
u8 tty;
|
||||
char* wayland_cmd;
|
||||
bool wayland_specifier;
|
||||
char* waylandsessions;
|
||||
char* x_cmd;
|
||||
char* x_cmd_setup;
|
||||
@@ -95,7 +102,7 @@ extern struct config config;
|
||||
|
||||
void config_handle_str(void* data, char** pars, const int pars_count);
|
||||
void lang_load();
|
||||
void config_load();
|
||||
void config_load(const char *cfg_path);
|
||||
void lang_defaults();
|
||||
void config_defaults();
|
||||
void lang_free();
|
||||
|
||||
+1
-2
@@ -11,7 +11,7 @@
|
||||
#include <fcntl.h>
|
||||
#include <stdlib.h>
|
||||
#include <string.h>
|
||||
#include <stropts.h>
|
||||
#include <sys/ioctl.h>
|
||||
#include <sys/stat.h>
|
||||
#include <unistd.h>
|
||||
|
||||
@@ -28,7 +28,6 @@ void draw_init(struct term_buf* buf)
|
||||
buf->width = tb_width();
|
||||
buf->height = tb_height();
|
||||
hostname(&buf->info_line);
|
||||
buf->info_line = NULL;
|
||||
|
||||
u16 len_login = strlen(lang.login);
|
||||
u16 len_password = strlen(lang.password);
|
||||
|
||||
@@ -115,6 +115,8 @@ void input_text(struct text* target, u64 len)
|
||||
target->end = target->text;
|
||||
target->visible_start = target->text;
|
||||
target->len = len;
|
||||
target->x = 0;
|
||||
target->y = 0;
|
||||
}
|
||||
|
||||
void input_desktop_free(struct desktop* target)
|
||||
@@ -256,3 +258,11 @@ void input_text_backspace(struct text* target)
|
||||
input_text_delete(target);
|
||||
}
|
||||
}
|
||||
|
||||
void input_text_clear(struct text* target)
|
||||
{
|
||||
memset(target->text, 0, target->len + 1);
|
||||
target->cur = target->text;
|
||||
target->end = target->text;
|
||||
target->visible_start = target->text;
|
||||
}
|
||||
@@ -50,5 +50,6 @@ void input_text_left(struct text* target);
|
||||
void input_text_write(struct text* target, char ascii);
|
||||
void input_text_delete(struct text* target);
|
||||
void input_text_backspace(struct text* target);
|
||||
void input_text_clear(struct text* target);
|
||||
|
||||
#endif
|
||||
+90
-57
@@ -18,6 +18,7 @@
|
||||
#include <sys/stat.h>
|
||||
#include <sys/wait.h>
|
||||
#include <unistd.h>
|
||||
#include <utmp.h>
|
||||
#include <xcb/xcb.h>
|
||||
|
||||
int get_free_display()
|
||||
@@ -204,11 +205,11 @@ void pam_diagnose(int error, struct term_buf* buf)
|
||||
dgn_throw(DGN_PAM);
|
||||
}
|
||||
|
||||
void env_init(struct passwd* pwd, const char* display_name)
|
||||
void env_init(struct passwd* pwd)
|
||||
{
|
||||
extern char** environ;
|
||||
// term
|
||||
char* term = getenv("TERM");
|
||||
char* lang = getenv("LANG");
|
||||
// clean env
|
||||
environ[0] = NULL;
|
||||
|
||||
@@ -226,9 +227,11 @@ void env_init(struct passwd* pwd, const char* display_name)
|
||||
setenv("SHELL", pwd->pw_shell, 1);
|
||||
setenv("USER", pwd->pw_name, 1);
|
||||
setenv("LOGNAME", pwd->pw_name, 1);
|
||||
setenv("DISPLAY", display_name, 1);
|
||||
setenv("LANG", lang, 1);
|
||||
|
||||
// path
|
||||
// Set PATH if specified in the configuration
|
||||
if (strlen(config.path))
|
||||
{
|
||||
int ok = setenv("PATH", config.path, 1);
|
||||
|
||||
if (ok != 0)
|
||||
@@ -236,6 +239,7 @@ void env_init(struct passwd* pwd, const char* display_name)
|
||||
dgn_throw(DGN_PATH);
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
void env_xdg(const char* tty_id, const enum display_server display_server)
|
||||
{
|
||||
@@ -250,7 +254,7 @@ void env_xdg(const char* tty_id, const enum display_server display_server)
|
||||
{
|
||||
case DS_WAYLAND:
|
||||
{
|
||||
setenv("XDG_SESSION_TYPE", "wayland", 0);
|
||||
setenv("XDG_SESSION_TYPE", "wayland", 1);
|
||||
break;
|
||||
}
|
||||
case DS_SHELL:
|
||||
@@ -267,11 +271,44 @@ void env_xdg(const char* tty_id, const enum display_server display_server)
|
||||
}
|
||||
}
|
||||
|
||||
void xauth(const char* display_name, const char* shell, const char* home)
|
||||
void add_utmp_entry(
|
||||
struct utmp *entry,
|
||||
char *username,
|
||||
pid_t display_pid
|
||||
) {
|
||||
entry->ut_type = USER_PROCESS;
|
||||
entry->ut_pid = display_pid;
|
||||
strcpy(entry->ut_line, ttyname(STDIN_FILENO) + strlen("/dev/"));
|
||||
|
||||
/* only correct for ptys named /dev/tty[pqr][0-9a-z] */
|
||||
strcpy(entry->ut_id, ttyname(STDIN_FILENO) + strlen("/dev/tty"));
|
||||
|
||||
time((long int *) &entry->ut_time);
|
||||
|
||||
strncpy(entry->ut_user, username, UT_NAMESIZE);
|
||||
memset(entry->ut_host, 0, UT_HOSTSIZE);
|
||||
entry->ut_addr = 0;
|
||||
setutent();
|
||||
|
||||
pututline(entry);
|
||||
}
|
||||
|
||||
void remove_utmp_entry(struct utmp *entry) {
|
||||
entry->ut_type = DEAD_PROCESS;
|
||||
memset(entry->ut_line, 0, UT_LINESIZE);
|
||||
entry->ut_time = 0;
|
||||
memset(entry->ut_user, 0, UT_NAMESIZE);
|
||||
setutent();
|
||||
pututline(entry);
|
||||
endutent();
|
||||
}
|
||||
|
||||
void xauth(const char* display_name, const char* shell, const char* dir)
|
||||
{
|
||||
char xauthority[256];
|
||||
snprintf(xauthority, 256, "%s/%s", home, ".lyxauth");
|
||||
snprintf(xauthority, 256, "%s/%s", dir, ".lyxauth");
|
||||
setenv("XAUTHORITY", xauthority, 1);
|
||||
setenv("DISPLAY", display_name, 1);
|
||||
|
||||
FILE* fp = fopen(xauthority, "ab+");
|
||||
|
||||
@@ -302,14 +339,21 @@ void xauth(const char* display_name, const char* shell, const char* home)
|
||||
|
||||
void xorg(
|
||||
struct passwd* pwd,
|
||||
const char* display_name,
|
||||
const char* vt,
|
||||
const char* desktop_cmd)
|
||||
{
|
||||
reset_terminal(pwd);
|
||||
|
||||
// generate xauthority file
|
||||
xauth(display_name, pwd->pw_shell, pwd->pw_dir);
|
||||
const char* xauth_dir = getenv("XDG_CONFIG_HOME");
|
||||
|
||||
if ((xauth_dir == NULL) || (*xauth_dir == '\0'))
|
||||
{
|
||||
xauth_dir = pwd->pw_dir;
|
||||
}
|
||||
|
||||
char display_name[4];
|
||||
|
||||
snprintf(display_name, 3, ":%d", get_free_display());
|
||||
xauth(display_name, pwd->pw_shell, xauth_dir);
|
||||
|
||||
// start xorg
|
||||
pid_t pid = fork();
|
||||
@@ -361,7 +405,6 @@ void xorg(
|
||||
|
||||
int status;
|
||||
waitpid(xorg_pid, &status, 0);
|
||||
reset_terminal(pwd);
|
||||
xcb_disconnect(xcb);
|
||||
kill(pid, 0);
|
||||
|
||||
@@ -376,28 +419,13 @@ void wayland(
|
||||
struct passwd* pwd,
|
||||
const char* desktop_cmd)
|
||||
{
|
||||
reset_terminal(pwd);
|
||||
pid_t pid = fork();
|
||||
|
||||
if (pid == 0)
|
||||
{
|
||||
char cmd[1024];
|
||||
snprintf(cmd, 1024, "%s %s", config.wayland_cmd, desktop_cmd);
|
||||
execl(pwd->pw_shell, pwd->pw_shell, "-c", cmd, NULL);
|
||||
exit(EXIT_SUCCESS);
|
||||
}
|
||||
|
||||
int status;
|
||||
waitpid(pid, &status, 0);
|
||||
reset_terminal(pwd);
|
||||
}
|
||||
|
||||
void shell(struct passwd* pwd)
|
||||
{
|
||||
reset_terminal(pwd);
|
||||
pid_t pid = fork();
|
||||
|
||||
if (pid == 0)
|
||||
{
|
||||
const char* pos = strrchr(pwd->pw_shell, '/');
|
||||
char args[1024];
|
||||
@@ -412,14 +440,26 @@ void shell(struct passwd* pwd)
|
||||
pos = pwd->pw_shell;
|
||||
}
|
||||
|
||||
strncpy(args + 1, pos, 1024);
|
||||
strncpy(args + 1, pos, 1023);
|
||||
execl(pwd->pw_shell, args, NULL);
|
||||
exit(EXIT_SUCCESS);
|
||||
}
|
||||
|
||||
int status;
|
||||
waitpid(pid, &status, 0);
|
||||
reset_terminal(pwd);
|
||||
// pam_do performs the pam action specified in pam_action
|
||||
// on pam_action fail, call diagnose and end pam session
|
||||
int pam_do(
|
||||
int (pam_action)(struct pam_handle *, int),
|
||||
struct pam_handle *handle,
|
||||
int flags,
|
||||
struct term_buf *buf)
|
||||
{
|
||||
int status = pam_action(handle, flags);
|
||||
|
||||
if (status != PAM_SUCCESS) {
|
||||
pam_diagnose(status, buf);
|
||||
pam_end(handle, status);
|
||||
}
|
||||
|
||||
return status;
|
||||
}
|
||||
|
||||
void auth(
|
||||
@@ -444,45 +484,36 @@ void auth(
|
||||
return;
|
||||
}
|
||||
|
||||
ok = pam_authenticate(handle, 0);
|
||||
ok = pam_do(pam_authenticate, handle, 0, buf);
|
||||
|
||||
if (ok != PAM_SUCCESS)
|
||||
{
|
||||
pam_diagnose(ok, buf);
|
||||
pam_end(handle, ok);
|
||||
return;
|
||||
}
|
||||
|
||||
ok = pam_acct_mgmt(handle, 0);
|
||||
ok = pam_do(pam_acct_mgmt, handle, 0, buf);
|
||||
|
||||
if (ok != PAM_SUCCESS)
|
||||
{
|
||||
pam_diagnose(ok, buf);
|
||||
pam_end(handle, ok);
|
||||
return;
|
||||
}
|
||||
|
||||
ok = pam_setcred(handle, PAM_ESTABLISH_CRED);
|
||||
ok = pam_do(pam_setcred, handle, PAM_ESTABLISH_CRED, buf);
|
||||
|
||||
if (ok != PAM_SUCCESS)
|
||||
{
|
||||
pam_diagnose(ok, buf);
|
||||
pam_end(handle, ok);
|
||||
return;
|
||||
}
|
||||
|
||||
ok = pam_open_session(handle, 0);
|
||||
ok = pam_do(pam_open_session, handle, 0, buf);
|
||||
|
||||
if (ok != PAM_SUCCESS)
|
||||
{
|
||||
pam_diagnose(ok, buf);
|
||||
pam_end(handle, ok);
|
||||
return;
|
||||
}
|
||||
|
||||
// clear the credentials
|
||||
input_text_free(password);
|
||||
input_text(password, config.max_password_len);
|
||||
input_text_clear(password);
|
||||
|
||||
// get passwd structure
|
||||
struct passwd* pwd = getpwnam(login->text);
|
||||
@@ -546,17 +577,14 @@ void auth(
|
||||
}
|
||||
|
||||
// get a display
|
||||
int display_id = get_free_display();
|
||||
char display_name[3];
|
||||
char tty_id [3];
|
||||
char vt[5];
|
||||
|
||||
snprintf(display_name, 3, ":%d", display_id);
|
||||
snprintf(tty_id, 3, "%d", config.tty);
|
||||
snprintf(vt, 5, "vt%d", config.tty);
|
||||
|
||||
// set env
|
||||
env_init(pwd, display_name);
|
||||
env_init(pwd);
|
||||
|
||||
if (dgn_catch())
|
||||
{
|
||||
@@ -583,6 +611,7 @@ void auth(
|
||||
exit(EXIT_FAILURE);
|
||||
}
|
||||
|
||||
reset_terminal(pwd);
|
||||
switch (desktop->display_server[desktop->cur])
|
||||
{
|
||||
case DS_WAYLAND:
|
||||
@@ -598,7 +627,7 @@ void auth(
|
||||
case DS_XINITRC:
|
||||
case DS_XORG:
|
||||
{
|
||||
xorg(pwd, display_name, vt, desktop->cmd[desktop->cur]);
|
||||
xorg(pwd, vt, desktop->cmd[desktop->cur]);
|
||||
break;
|
||||
}
|
||||
}
|
||||
@@ -606,9 +635,16 @@ void auth(
|
||||
exit(EXIT_SUCCESS);
|
||||
}
|
||||
|
||||
// add utmp audit
|
||||
struct utmp entry;
|
||||
add_utmp_entry(&entry, pwd->pw_name, pid);
|
||||
|
||||
// wait for the session to stop
|
||||
int status;
|
||||
waitpid(pid, &status, 0);
|
||||
remove_utmp_entry(&entry);
|
||||
|
||||
reset_terminal(pwd);
|
||||
|
||||
// reinit termbox
|
||||
tb_init();
|
||||
@@ -620,21 +656,17 @@ void auth(
|
||||
desktop_load(desktop);
|
||||
|
||||
// close pam session
|
||||
ok = pam_close_session(handle, 0);
|
||||
ok = pam_do(pam_close_session, handle, 0, buf);
|
||||
|
||||
if (ok != PAM_SUCCESS)
|
||||
{
|
||||
pam_diagnose(ok, buf);
|
||||
pam_end(handle, ok);
|
||||
return;
|
||||
}
|
||||
|
||||
ok = pam_setcred(handle, PAM_DELETE_CRED);
|
||||
ok = pam_do(pam_setcred, handle, PAM_DELETE_CRED, buf);
|
||||
|
||||
if (ok != PAM_SUCCESS)
|
||||
{
|
||||
pam_diagnose(ok, buf);
|
||||
pam_end(handle, ok);
|
||||
return;
|
||||
}
|
||||
|
||||
@@ -645,3 +677,4 @@ void auth(
|
||||
pam_diagnose(ok, buf);
|
||||
}
|
||||
}
|
||||
|
||||
+49
-30
@@ -16,10 +16,9 @@
|
||||
#include <unistd.h>
|
||||
#include <stdlib.h>
|
||||
|
||||
#define ARG_COUNT 5
|
||||
#define ARG_COUNT 7
|
||||
// things you can define:
|
||||
// GIT_VERSION_STRING
|
||||
// RUNIT
|
||||
|
||||
// global
|
||||
struct lang lang;
|
||||
@@ -61,6 +60,11 @@ void log_init(char** log)
|
||||
log[DGN_HOSTNAME] = lang.err_hostname;
|
||||
}
|
||||
|
||||
void arg_config(void* data, char** pars, const int pars_count)
|
||||
{
|
||||
*((char **)data) = *pars;
|
||||
}
|
||||
|
||||
// ly!
|
||||
int main(int argc, char** argv)
|
||||
{
|
||||
@@ -71,17 +75,13 @@ int main(int argc, char** argv)
|
||||
config_defaults();
|
||||
lang_defaults();
|
||||
|
||||
config_load();
|
||||
|
||||
if (strcmp(config.lang, "en") != 0)
|
||||
{
|
||||
lang_load();
|
||||
}
|
||||
|
||||
char *config_path = NULL;
|
||||
// parse args
|
||||
const struct argoat_sprig sprigs[ARG_COUNT] =
|
||||
{
|
||||
{NULL, 0, NULL, NULL},
|
||||
{"config", 0, &config_path, arg_config},
|
||||
{"c", 0, &config_path, arg_config},
|
||||
{"help", 0, NULL, arg_help},
|
||||
{"h", 0, NULL, arg_help},
|
||||
{"version", 0, NULL, arg_version},
|
||||
@@ -106,6 +106,13 @@ int main(int argc, char** argv)
|
||||
return 1;
|
||||
}
|
||||
|
||||
config_load(config_path);
|
||||
|
||||
if (strcmp(config.lang, "en") != 0)
|
||||
{
|
||||
lang_load();
|
||||
}
|
||||
|
||||
void* input_structs[3] =
|
||||
{
|
||||
(void*) &desktop,
|
||||
@@ -196,45 +203,49 @@ int main(int argc, char** argv)
|
||||
|
||||
if (event.type == TB_EVENT_KEY)
|
||||
{
|
||||
if (event.key == TB_KEY_F1)
|
||||
switch (event.key)
|
||||
{
|
||||
case TB_KEY_F1:
|
||||
shutdown = true;
|
||||
run = false;
|
||||
break;
|
||||
}
|
||||
else if (event.key == TB_KEY_F2)
|
||||
{
|
||||
case TB_KEY_F2:
|
||||
reboot = true;
|
||||
run = false;
|
||||
break;
|
||||
}
|
||||
else if (event.key == TB_KEY_CTRL_C)
|
||||
case TB_KEY_CTRL_C:
|
||||
run = false;
|
||||
break;
|
||||
case TB_KEY_CTRL_U:
|
||||
if (active_input > 0)
|
||||
{
|
||||
break;
|
||||
input_text_clear(input_structs[active_input]);
|
||||
}
|
||||
else if ((event.key == TB_KEY_ARROW_UP) && (active_input > 0))
|
||||
break;
|
||||
case TB_KEY_ARROW_UP:
|
||||
if (active_input > 0)
|
||||
{
|
||||
--active_input;
|
||||
update = true;
|
||||
}
|
||||
else if (((event.key == TB_KEY_ARROW_DOWN)
|
||||
|| (event.key == TB_KEY_ENTER))
|
||||
&& (active_input < 2))
|
||||
break;
|
||||
case TB_KEY_ARROW_DOWN:
|
||||
if (active_input < 2)
|
||||
{
|
||||
++active_input;
|
||||
update = true;
|
||||
}
|
||||
else if (event.key == TB_KEY_TAB)
|
||||
{
|
||||
break;
|
||||
case TB_KEY_TAB:
|
||||
++active_input;
|
||||
|
||||
if (active_input > 2)
|
||||
{
|
||||
active_input = 0;
|
||||
active_input = PASSWORD_INPUT;
|
||||
}
|
||||
|
||||
update = true;
|
||||
}
|
||||
else if (event.key == TB_KEY_ENTER)
|
||||
{
|
||||
break;
|
||||
case TB_KEY_ENTER:
|
||||
save(&desktop, &login);
|
||||
auth(&desktop, &login, &password, &buf);
|
||||
update = true;
|
||||
@@ -242,12 +253,19 @@ int main(int argc, char** argv)
|
||||
if (dgn_catch())
|
||||
{
|
||||
++auth_fails;
|
||||
// move focus back to password input
|
||||
active_input = PASSWORD_INPUT;
|
||||
|
||||
if (dgn_output_code() != DGN_PAM)
|
||||
{
|
||||
buf.info_line = dgn_output_log();
|
||||
}
|
||||
|
||||
if (config.blank_password)
|
||||
{
|
||||
input_text_clear(&password);
|
||||
}
|
||||
|
||||
dgn_reset();
|
||||
}
|
||||
else
|
||||
@@ -256,13 +274,14 @@ int main(int argc, char** argv)
|
||||
}
|
||||
|
||||
load(&desktop, &login);
|
||||
}
|
||||
else
|
||||
{
|
||||
system("tput cnorm");
|
||||
break;
|
||||
default:
|
||||
(*input_handles[active_input])(
|
||||
input_structs[active_input],
|
||||
&event);
|
||||
update = true;
|
||||
break;
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
+31
@@ -95,6 +95,19 @@ void desktop_crawl(
|
||||
strncat(path, dir_info->d_name, (sizeof (path)) - 1);
|
||||
configator(&desktop_config, path);
|
||||
|
||||
// if these are wayland sessions, add " (Wayland)" to their names,
|
||||
// as long as their names don't already contain that string
|
||||
if (server == DS_WAYLAND && config.wayland_specifier)
|
||||
{
|
||||
const char wayland_specifier[] = " (Wayland)";
|
||||
if (strstr(name, wayland_specifier) == NULL)
|
||||
{
|
||||
name = realloc(name, (strlen(name) + sizeof(wayland_specifier) + 1));
|
||||
// using strcat is safe because the string is constant
|
||||
strcat(name, wayland_specifier);
|
||||
}
|
||||
}
|
||||
|
||||
if ((name != NULL) && (exec != NULL))
|
||||
{
|
||||
input_desktop_add(target, name, exec, server);
|
||||
@@ -110,8 +123,26 @@ void desktop_crawl(
|
||||
|
||||
void desktop_load(struct desktop* target)
|
||||
{
|
||||
// we don't care about desktop environments presence
|
||||
// because the fallback shell is always available
|
||||
// so we just dismiss any "throw" for now
|
||||
int err = 0;
|
||||
|
||||
desktop_crawl(target, config.waylandsessions, DS_WAYLAND);
|
||||
|
||||
if (dgn_catch())
|
||||
{
|
||||
++err;
|
||||
dgn_reset();
|
||||
}
|
||||
|
||||
desktop_crawl(target, config.xsessions, DS_XORG);
|
||||
|
||||
if (dgn_catch())
|
||||
{
|
||||
++err;
|
||||
dgn_reset();
|
||||
}
|
||||
}
|
||||
|
||||
static char* hostname_backup = NULL;
|
||||
|
||||
+1
-1
Submodule sub/argoat updated: 36c41f09ec...76d1e23b5e.
+1
-1
Submodule sub/configator updated: 22ce943e65...8cec178619.
+1
-1
Submodule sub/ctypes updated: 5dd979d364...eb4b36559d.
+1
-1
Submodule sub/dragonfail updated: 6b40d1f8b7...0a2492c6aa.
+1
-1
Submodule sub/termbox_next updated: d356892786...23fff64470.
Reference in new issue
Block a user